Empowering your employees for better information security
Your colleagues are the backbone of your organisation, working tirelessly to drive success. But let’s face it: where there are people, there’s always the risk for human error. And when it comes to information security, human behaviour remains one of the the biggest risk factors.
Your employees hold the keys to the kingdom. Depending on their role, they may have access to sensitive company data, customer information, and financial records. But are they aware of the responsibility this entails? And, more importantly, are they vigilant enough to protect these critical assets from potential threats?
Information security is all about safeguarding confidential and sensitive information. Achieving this requires a balanced focus on three key elements:
One element cannot function effectively without the others. A strong policy means little if employees don’t follow protocols, and technical solutions are useless if staff are careless with passwords or access management.
In short, human behaviour is the most vulnerable factor in information security. Cybercriminals know this and exploit it through social engineering tactics, manipulating emotions and behaviour to gain access to sensitive data or compel certain actions. Attacking the human element is often more effective than targeting technical defences, requiring less expertise and yielding quicker results.

An unaware employee fell for malware
A recent large-scale data breach occurred at a Dutch police department when a volunteer clicked on a malicious link. While there were many contributing factors, the crux of the issue was a lack of awareness and training, leaving the individual unable to recognise the threat.
Deepfake technology duped an employee
In one case, a staff member transferred the equivalent of €24 million to criminals after receiving a phishing email. A sophisticated deepfake video convinced the employee they were dealing with colleagues, leading to the fraudulent transaction.
Deliberate Data Leaks by Disgruntled Employees
Data breaches aren’t always accidental. Sometimes, ex-employees intentionally leak sensitive information, as seen in a Tesla case in 2023, or the incident at Radboud University Medical Centre in 2021, where a former employee shared confidential data on GitHub.
Unfortunately, many companies fail to implement sufficient security measures to prevent incidents. Use the tips below to reduce the risks and strengthen your organisation's security.
Effective information security is achieved when people, policies, and technology work together in harmony. Provide your employees with the right technical tools to work securely, such as password managers. Ensure that your organisation has clear policies and protocols in place. You can also use technical solutions like firewalls to protect sensitive data from threats and prevent unauthorised access. However, it’s important to remember that technical measures alone won’t suffice without alert and aware employees.
Clear communication about security awareness is essential to keep the topic relevant and top of mind. This starts as early as onboarding new employees, when you introduce them to your organisation’s code of conduct, and continues through to their offboarding, when you discuss guidelines for safely returning company assets.
Ensure that all communication is easy to understand and accessible to everyone. Avoid setting unrealistic expectations and use simple, jargon-free language to make the message clear.
Creating an open reporting culture is also vital. You don’t want employees to feel embarrassed or afraid to report suspicious situations. Let them know that proactive action is appreciated and can prevent greater harm. Encourage them to report incidents promptly and reward those who do.
Most people are likely to point to the IT department when asked who is responsible for information security. In reality, information security is a shared responsibility across the entire organisation. The challenge is that many employees aren’t aware of this or don’t see it as their responsibility.
These tips will help you easily involve all your colleagues in the process.
A crucial component of strong information security is security awareness training. This empowers employees to become the strongest link in your organisation’s security chain. Regular training fosters long-term protection against online risks and threats.
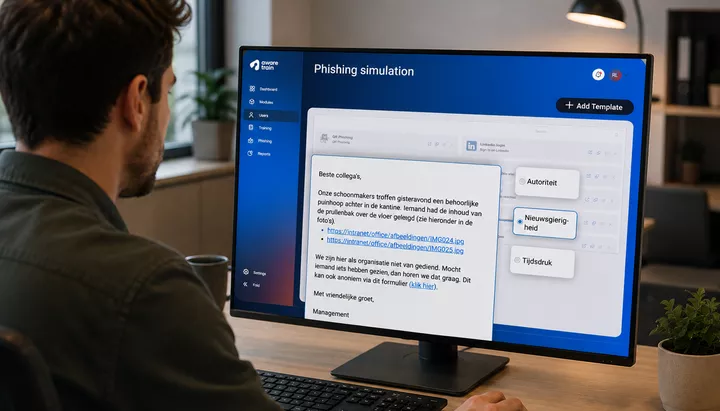
With the Awaretrain platform, you can train your colleagues in security awareness in a fun and easy way. Sign up for a free trial to explore our extensive content library packed with interactive games, bite-sized security tips, and engaging challenges. Create customised training programmes with ease and see how effortless it is to train your entire organisation—no matter where they are in the world.
Awareness is the first step toward changing behaviour and preventing incidents. While no organisation can achieve 100% perfect security, every click, every decision, and every bit of awareness moves your organisation closer to strong security.
Are your employees the weakest link or your greatest strength in information security? Discover how to minimise risks and empower your team to take action.
Training modules
Customers worldwide
Employees trained

Step aboard and build lasting security awareness with Awaretrain.